Synthetic identity fraud ai customer onboarding systems face an aggressive wave of automated attacks. Criminal rings no longer rely on stolen wallets or crude physical document scans. Instead, they combine real Social Security numbers stolen from credit bureaus with diffusion-generated driver licenses, algorithmic facial deepfakes, and programmatically nurtured credit histories. When mid-market lenders, credit unions, equipment leasing firms, and regional fintechs switch to automated digital verification pipelines, legacy Know Your Customer (KYC) rules fail to catch these hybrid fabrications.
The financial fallout is severe. Traditional identity theft triggers immediate fraud alerts because genuine account holders report unauthorized charges within thirty days. Synthetic identity fraud behaves differently. Criminal syndicates cultivate fabricated identities for twelve to twenty-four months, building prime credit ratings through small recurring payments before orchestrating simultaneous loan drawdowns across multiple regional institutions. By the time write-offs hit default reserves, the perpetrators have vanished.
Protecting automated customer intake pipelines requires modern verification controls that inspect machine learning document artifacts, enforce hardware-anchored biometric liveness, and cross-reference multi-bureau credit depth.

How Do Fraudsters Use Generative AI for Synthetic Identity Fraud?
Modern synthetic identity creation is an industrial operation. Criminals combine legitimate Personally Identifiable Information (PII), frequently harvested from minors, deceased citizens, or elderly individuals without active credit files, with fabricated personal histories generated by commercial AI tools:
| Attack Progression Stage | Fraud Syndicate Methodology | Underlying AI / Technological Vector | Forensic Identification Marker |
|---|---|---|---|
| Stage 1: Identity Synthesis | Pair unassigned / child SSN with fabricated personal details | Diffusion models rendering driver licenses & utility statements | High-frequency Fourier halo, broken guilloche lines |
| Stage 2: Credit File Cultivation | Purchase authorized-user tradelines on seasoned accounts | Underground piggybacking broker networks (12-24 months) | Discrepancy between tradeline maturity and applicant age |
| Stage 3: Account Application | Submit concurrent digital applications to credit unions & fintechs | Virtual camera emulation (OBS, WebRTC injection hooks) | Uniform screen reflectance, failure of active chromatic flash |
| Stage 4: Bust-Out Liquidation | Maximize line draws, cash advances, and equipment loans | Automated bots coordinating rapid cross-lender withdrawals | Velocity surge on shared CMRA address or virtual VoIP number |
1. High-Fidelity Diffusion Document Synthesis
Fraud networks run fine-tuned Stable Diffusion and Flux models trained on tens of thousands of state driver licenses, passports, and utility bills. These tools render state-specific guilloche patterns, holographic overlays, and microprint text with sub-pixel precision. When paired with automated PDF generators that synthesize realistic utility bills matching local municipal utility districts, initial optical character recognition (OCR) systems approve the documents without suspicion.
2. Camera Stream Injection and Virtual Drivers
Rather than pointing a smartphone camera at a physical computer monitor displaying a stolen photograph, attackers route synthetic video through software camera emulators (such as OBS Virtual Camera) or custom mobile device operating system hooks. The fake video feed injects generated frames directly into the mobile browser’s WebRTC media pipeline, bypassing standard optical liveness checks.
3. Credit File Cultivation via Authorized User Piggybacking
Once a synthetic identity pairs an unassigned or dormant Social Security number with a generated name, fraudsters purchase authorized user slots on seasoned revolving credit accounts through underground brokering networks. Within six months, national credit bureaus generate a credit profile. The synthetic identity reaches a 720 FICO score before submitting automated loan applications to mid-market financial institutions.
Much like enterprise account takeover schemes documented in our small business cybersecurity checklist, automated synthetic identity attacks exploit institutional reliance on digital verification checks that lack hardware attestation.
Diffusion Model Document Forgery: Digital Breadcrumb Analysis
Automated customer onboarding platforms must move past simple text extraction OCR. Machine-generated identity documents exhibit mathematical anomalies invisible to human reviewers but detectable through algorithmic document forensics:
| Inspection Vector | Genuine Physical Credential | Generative AI / Diffusion Credential | Algorithmic Inspection Technique |
|---|---|---|---|
| Microprint Typography | Crisp vector edges stamped at 600+ DPI | Blurry pixel clustering, character morphing | High-frequency spatial Fourier transform |
| Guilloche Fine Lines | Continuous unbroken mathematical curves | Broken raster lines, pixelated intersections | Gradient vector flow boundary analysis |
| Ghost Portrait Opacity | Laser-perforated or UV variable density | Flat alpha-channel blending layer | Specular reflection cross-polarization |
| Image EXIF / Metadata | Raw sensor color profiles, OEM metadata | Canvas export headers, missing ICC profile | Forensic header and quantization audit |
| Barcode Data Matrix | PDF417 binary payload matching front text | Discrepant delimiters, mismatched dates | Structured AAMVA standard parsing |
Fourier Domain Artifact Detection
Diffusion models reconstruct images from Gaussian noise vectors. While they reproduce macroscopic shapes accurately, they struggle with high-frequency spatial frequencies. Running a fast Fourier transform (FFT) across background security patterns reveals distinctive spectral halos common to latent diffusion decoders. When an uploaded identity credential exhibits these periodic frequency spikes, the intake system flags the application for mandatory secondary physical review.
PDF417 Barcode and Front-Face Triangulation
State-issued identification cards encode driver demographic information within a high-density PDF417 two-dimensional barcode on the reverse side. Attackers using image generators frequently create front-facing identification cards that look authentic but pair them with generic or improperly formatted barcodes borrowed from other credentials. Comparing the machine-readable zone (MRZ) or PDF417 payload fields against front-face OCR data detects synthetic fabrications instantly.
What Detection Methods Stop Deepfake Face Liveness Bypasses?
Biometric selfie verification is standard in digital customer onboarding. However, passive liveness models that merely check for an open eye or a static smile fail against real-time deepfake video streams. Defending against modern biometric spoofing requires active, multi-modal challenges:
1. Chromatic Flash Reflection Analysis
During the selfie verification session, the onboarding application flashes pseudo-random sequences of colored screen illumination (e.g., violet, amber, teal) across the applicant’s face. The verification engine analyzes the physiological reflection patterns across the skin’s surface:
Frame t+0: Display emits #8A2BE2 (Violet)  -> Skin reflectance responds in blue-red channel
Frame t+1: Display emits #FFBF00 (Amber)   -> Skin reflectance responds in red-green channel
Frame t+2: Display emits #008080 (Teal)    -> Skin reflectance responds in green channel
A deepfake generator running over a virtual camera driver cannot predict the millisecond screen flash sequence in advance. Synthetic video streams display uniform, static lighting that fails the photometric correlation check.
2. WebAuthn Hardware Cryptographic Attestation
To prevent virtual camera injection, mid-market fintechs require applicants to register using mobile browsers that support FIDO2 and WebAuthn hardware device attestation. By anchoring the customer’s onboarding session to physical secure enclaves (such as Apple Secure Enclave or Android StrongBox), the application guarantees that video capture originates from verified physical camera hardware rather than an emulated software driver. This hardware-anchored defense mirrors best practices outlined in our two-factor authentication implementation guide.
3. Spatial Mesh Depth Mapping
Passive 2D photographs projected on flat monitors or tablet screens lack three-dimensional facial topology. Modern onboarding SDKs utilize dual-camera arrays and LiDAR sensors present in modern smartphones to construct a 3D polygonal point cloud of the applicant’s nose bridge, cheekbones, and jawline. Replayed video and screen projections fail depth thresholds immediately.
Multi-Bureau Synthetic Credit Profile Triangulation
Synthetic identities often bypass initial credit bureau checks because they possess valid credit scores. What they lack is historical depth and authentic consumer interaction patterns.
Mid-market compliance teams integrate automated graph database queries across Experian, Equifax, TransUnion, and alternative consumer databases to identify synthetic profiles:
Social Security Number Issuance Date Anomalies
Prior to June 2011, the Social Security Administration (SSA) issued Social Security numbers using geographical area numbers and predictable sequence pools. In June 2011, the SSA transitioned to randomized SSN issuance. If an onboarding applicant claims to be forty-five years old but presents an SSN issued under the post-2011 randomized pool, the application represents a synthetic fabrication.
Electronic Consent Based Social Security Number Verification (eCBSV)
The federal Social Security Administration operates the eCBSV automated API, allowing participating financial institutions to verify whether an applicant’s name, SSN, and date of birth match official federal records. Integrating eCBSV into automated onboarding workflows neutralizes synthetic identities constructed using dormant child or deceased person identifiers.
Phone Number and Physical Address Velocity
Fraudsters maximize return on effort by recycling virtual phone numbers, commercial mail drop addresses, and residential forwarding suites across dozens of synthetic accounts. Querying telecom carrier APIs reveals whether a mobile phone number belongs to a prepaid burner line, a VoIP routing proxy, or a postpaid carrier account with years of continuous billing history.
Institutions managing these multi-layered data pipelines must ensure automated verification processes comply with consumer privacy frameworks, as examined in our analysis of AI compliance automation for SOC 2, HIPAA, and GDPR. Furthermore, the Federal Trade Commission consistently advises financial institutions to monitor credit profile fragmentation as a primary indicator of organized synthetic bust-out schemes.
How Do Mid-Market Fintechs Prevent Synthetic Onboarding Fraud?
Mid-market financial organizations cannot afford the seven-figure fraud defense infrastructures maintained by tier-one global banks. However, adopting a risk-tiered step-up architecture provides institutional-grade protection without degrading conversion rates for legitimate customers:
{
  "onboarding_event_id": "kyc_triage_2026_9941c",
  "timestamp": "2026-10-14T11:42:09.114Z",
  "applicant_metadata": {
    "claimed_name": "Evelyn R. Vance",
    "ssn_sequence_hash": "a8f3b20c4e1298d01b44...",
    "claimed_dob": "1982-04-12",
    "phone_number": "+1-512-555-0194"
  },
  "passive_telemetry_findings": {
    "ip_routing_type": "DATA_CENTER_PROXY_HOSTING",
    "device_webrtc_camera_driver": "v4l2loopback_virtual_device",
    "form_paste_latency_ms": 42,
    "passive_risk_tier": "ELEVATED_STEP_UP_MANDATED"
  },
  "step_up_investigation_results": {
    "document_forensics": {
      "credential_type": "TEXAS_COMMERCIAL_DRIVER_LICENSE",
      "fft_spectral_peak_anomaly": true,
      "pdf417_barcode_mismatch": true,
      "discrepancy_details": "Barcode encodes 1994 birth year vs front OCR 1982"
    },
    "biometric_liveness_challenge": {
      "active_chromatic_flash_sequence": ["VIOLET_8A2BE2", "AMBER_FFBF00", "TEAL_008080"],
      "photometric_reflectance_variance": 0.04,
      "liveness_verdict": "FAIL_SYNTHETIC_DEEPFAKE_INJECTION"
    },
    "federal_ecbsv_attestation": {
      "ssa_name_ssn_match": false,
      "social_security_death_index_match": false,
      "ssn_issuance_year": 2014,
      "ssn_age_mismatch_years": 32
    }
  },
  "automated_decision": {
    "intake_status": "REJECTED_SYNTHETIC_IDENTITY_FRAUD",
    "internal_fraud_ledger_logged": true,
    "cross_product_quarantine_active": true
  }
}
1. Passive Behavioral Telemetry
Before an applicant uploads a single document, client-side software monitors form interaction dynamics:
- Did the user paste their Social Security number and legal name from a clipboard within four hundred milliseconds, indicating automated bot distribution?
- Does the device screen resolution match the graphics rendering engine reported by WebGL?
- Is the applicant connecting through a commercial data center IP address rather than a residential ISP?
2. Dynamic Step-Up Triggers
Rather than subjecting ninety-five percent of low-risk legitimate applicants to exhaustive identity audits, the onboarding engine triggers step-up verification only when passive telemetry detects risk indicators. An applicant presenting a VoIP telephone number, a recent address change, or a thin credit file is directed to complete chromatic flash liveness verification and eCBSV authentication.
3. Cross-Department Fraud Data Sharing
Synthetic identities often strike multiple departments within the same mid-market institution. A credit union might see a synthetic profile open a basic savings account in March, apply for an auto loan in June, and request a commercial equipment lease in October. Establishing a unified customer risk registry prevents fragmented departments from reviewing applications in isolation.
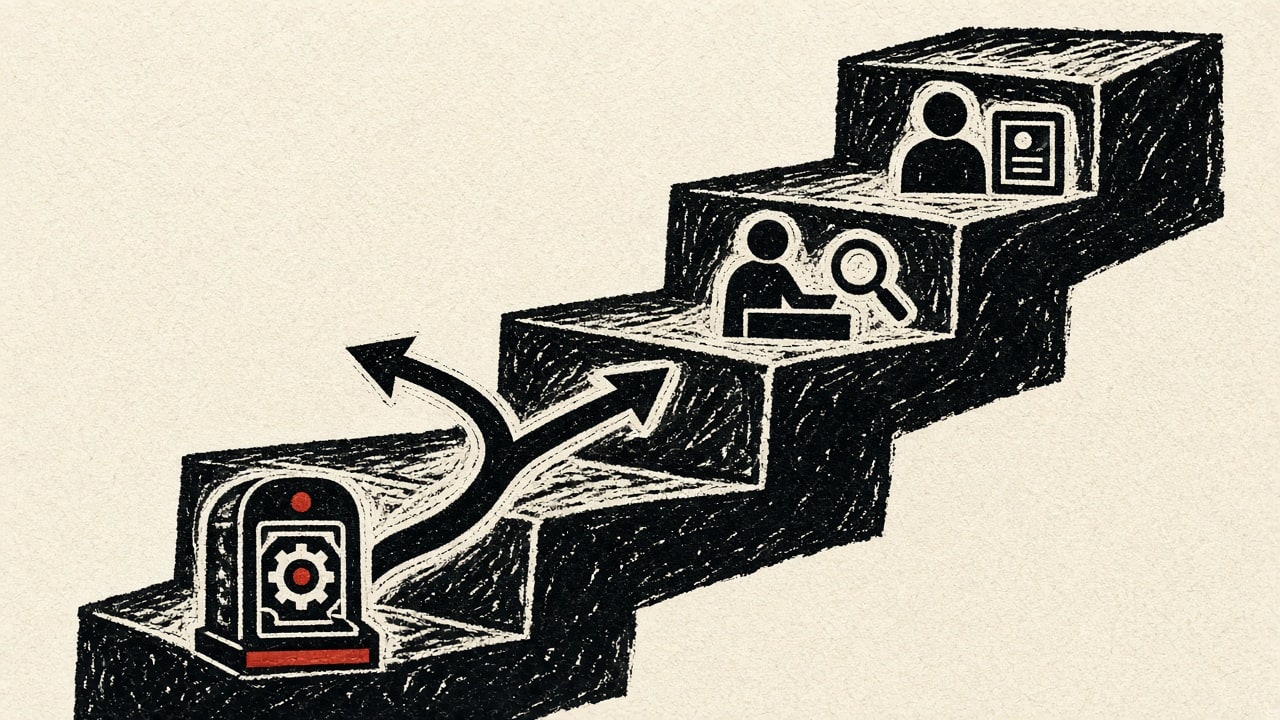
Synthetic Identity Fraud Defense Protocol
Chief risk officers, compliance directors, and fraud engineering leads should establish a multi-tier synthetic fraud containment protocol across four operational tiers:
Tier 1: Passive Behavioral Telemetry and Device Attestation
- Inspect client-side behavioral dynamics, flagging clipboard paste speeds faster than human typing capabilities.
- Enforce WebAuthn and FIDO2 hardware cryptographic attestation to confirm camera feeds originate from physical sensors.
- Detect virtual camera software drivers (such as OBS Virtual Camera or v4l2loopback) and terminate emulated media streams.
Tier 2: Fourier Document Forensics and Barcode Triangulation
- Apply high-frequency Fast Fourier Transform (FFT) analysis across identity card backgrounds to detect latent diffusion rendering patterns.
- Decode high-density PDF417 two-dimensional barcodes and compare payload data fields against front-face OCR extractions.
- Cross-reference physical street addresses against national registries of Commercial Mail Receiving Agencies (CMRA) and forwarding hubs.
Tier 3: Active Photometric Biometrics and Depth Mapping
- Execute active chromatic flash challenges during selfie sessions, measuring skin reflectance against randomized millisecond color sequences.
- Utilize smartphone LiDAR or stereoscopic depth mapping to verify authentic 3D facial topology and reject 2D screen replays.
- Screen incoming telephone numbers through carrier APIs to block VoIP proxies, burner numbers, and recent SIM swaps.
Tier 4: Federal eCBSV Verification and Institutional Ledger Sharing
- Integrate official Social Security Administration eCBSV API calls to verify name, Social Security number, and birth date combinations.
- Filter out artificial credit score cultivation by discounting authorized-user tradelines on thin-file credit applicants.
- Maintain a unified internal fraud registry across deposit, lending, and leasing departments to prevent multi-product bust-out schemes.
Conclusion
Automated customer onboarding delivers significant operational advantages, reducing account opening friction from several business days to under ninety seconds. However, deploying AI verification models without rigorous forensic safeguards creates an open gateway for organized synthetic fraud rings.
Generative AI tools make the fabrication of high-fidelity credentials, convincing facial video, and synthetic credit histories trivial for criminal syndicates. To protect loan portfolios and maintain regulatory compliance, mid-market financial institutions must deploy defense-in-depth verification architectures. By pairing Fourier document analysis and hardware-anchored biometric liveness with federal SSN validation and behavioral telemetry, organizations eliminate synthetic identity vulnerabilities while maintaining a frictionless onboarding experience for legitimate customers.